This article explains what a cyber incident is and what you should do if your school or trust experiences one. A cyber incident isn't necessarily a full-blown cyber attack, but it should still go through your reporting and risk management processes.
Cyber incidents and attacks can have significant operational and financial impacts on schools, trusts and other organisations. They are often intentional and unauthorised attempts to access, change or damage data and digital technology, and they could be made by a person, group or organisation outside or inside your organisation.
Please note: the attempt does not need to be successful for it to count as a cyber incident.
Ways to protect against and prevent cyber incidents
- Conduct regular cyber risk assessments and review them. Our free Cyber Risk Register can help you get started.
- Create and implement a cyber awareness plan for staff.
- Secure technology and data with anti-malware and a firewall.
- Control and secure user accounts and access privileges, including multi-factor authentication (MFA).
- License digital technology and keep it up to date.
- Develop and implement a plan to back up your data, and review it regularly.
- Filter and monitor your systems.
- Have an internal process for reporting and recording cyber incidents and attacks.
An example of a cyber incident
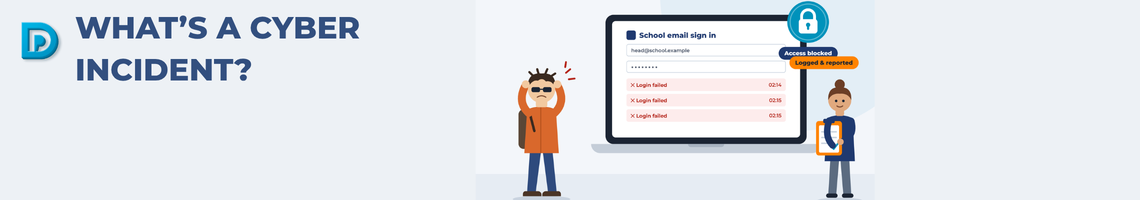
Your email system receives repeated login attempts using staff names and contact details taken from your website or social media. None of the attempts succeed, but this is still a cyber incident. In response, you should:
- make sure MFA is set up on all cloud accounts that hold personal data
- restrict any other method of remote access, such as Remote Desktop Services (RDS)
- reset passwords if necessary
- record the incident in your internal incident log.
You can then use the incident to confirm to SLT that your systems are robust, or to review how they could be improved.
Guidance and free support
- Schools and colleges should refer to the DfE cyber security standards for schools and colleges.
- The DfE Cyber Security Hub has step-by-step incident playbooks for ransomware, business email compromise and extortion via AI, plus an incident response process and communication templates for staff, parents and the media.
- Whatever kind of organisation you are, consider joining Police CyberAlarm, a free, Home Office-funded service that monitors your internet connection for suspicious activity and sends you regular reports.
What to do in the event of a cyber attack
First, follow your cyber response plan. Record the incident in your internal incident log, inform your governing board or trustees, and contact your Data Protection Officer (DPO) as soon as possible if personal data could be involved.
Incidents or attacks where a security breach may have taken place, or other damage was caused, should also be reported to an external body. The SLT digital lead is responsible for assigning someone to report any suspicious cyber incidents or attacks. This person will need to report to:
- Report Fraud, which replaced Action Fraud in December 2025, on 0300 123 2040 or through the Report Fraud website. Make sure it is recorded as a crime report so that you receive a crime reference number.
- the DfE sector cyber team at
This email address is being protected from spambots. You need JavaScript enabled to view it.
You may also need to report to:
- the National Cyber Security Centre (NCSC) if the incident or attack causes long-term school closure, the closure of more than one school, or serious financial damage. If you're not sure who to report to, use the government's cyber incident signposting service.
- the Information Commissioner's Office (ICO) within 72 hours of becoming aware of a personal data breach, unless the breach is unlikely to result in a risk to people's rights and freedoms. If the risk is high, you must also tell the people affected without undue delay. Your DPO can help you assess this. We will do this on behalf of DPE customers.
- the Risk Protection Arrangement (RPA) emergency assistance helpline on 0800 368 6378 or
This email address is being protected from spambots. You need JavaScript enabled to view it. , if you are an RPA member, or your cyber insurance provider if you have one - your local police force if you suspect a safeguarding impact
- any third-party service providers whose systems are affected, so they can be part of a coordinated response
- Jisc CSIRT, if you are part of a further education institution.
You must act in accordance with:
- Report Fraud's guide to reporting cyber crime and fraud
- Academy Trust Handbook Part 6, if you are part of an academy trust. Since September 2025, academy trusts must not pay any cyber ransom demands.
- the ICO's guidance on personal data breaches.
Preserve the evidence
Police investigations may find out whether any compromised data has been published or sold, and identify the perpetrator. Preserving evidence is as important as recovering from the crime. Keep a clear record of what happened, when, and what actions you took. The DfE's guidance on record keeping in an incident explains what to capture.
Reporting suspicious emails and texts
Forward suspicious emails to